What Security Tradeoff Occurs While Using IDS in 2026? Explained Simply
 Hardik Gupta25 Sept, 2026
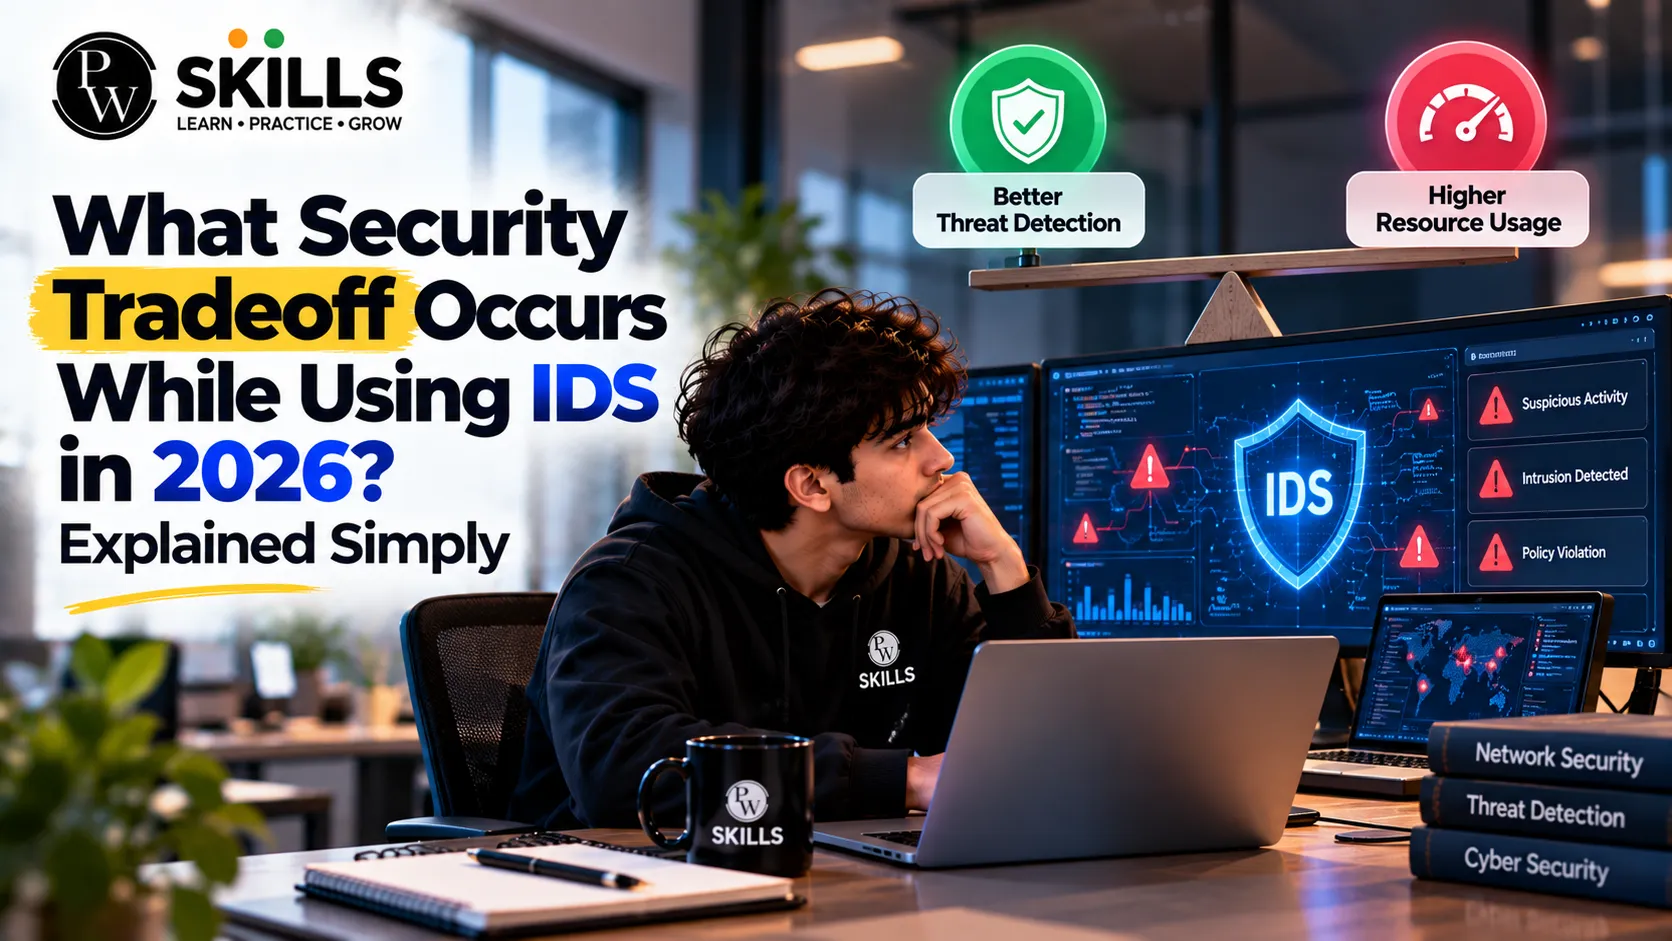
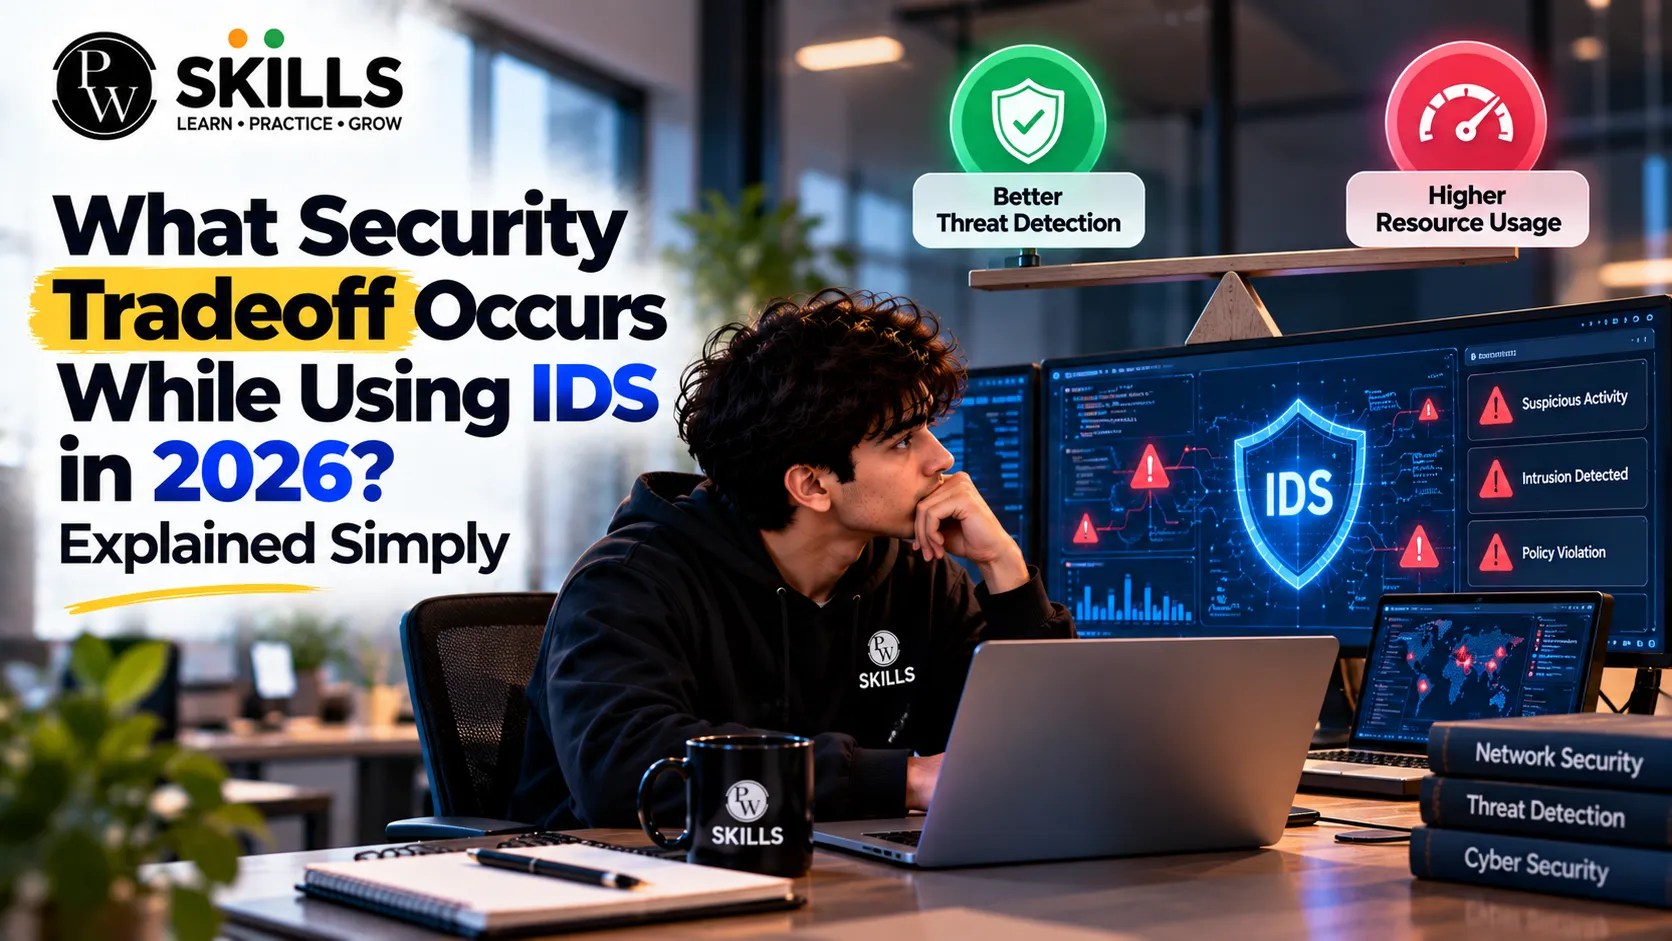
Understanding what security tradeoff occurs while using IDS is important for anyone learning network security. An Intrusion Detection System (IDS) helps organizations monitor network traffic and identify suspicious activity.
However, using an IDS also creates certain challenges. An IDS must inspect large amounts of network traffic and generate alerts when it finds unusual behavior. More detailed monitoring can improve threat detection, but it can also increase system workload and create more alerts for security teams to review.
What Security Tradeoff Occurs While Using IDS in Network Security?
To understand what security tradeoff occurs in IDS, it is important to know how an IDS works. An IDS monitors network activity and looks for signs of attacks, unauthorized access, or unusual behavior.
It can use different methods to identify threats:
-
Traffic monitoring: Examines network activity for suspicious behavior.
-
Signature detection: Compares activity with patterns of known attacks.
-
Anomaly detection: Looks for behavior that is different from the normal network baseline.
Better monitoring can provide greater visibility into threats. However, checking more traffic and using more detection rules can require additional processing power and create more alerts.
This creates a basic tradeoff between detection coverage and operational efficiency.
What are the IDS Security Tradeoffs in Real-World Networks?
The main answer to what security tradeoffs occur while using IDS is that organizations must balance security visibility, detection accuracy, system resources, and analyst workload.
A highly sensitive IDS may detect more suspicious activity, but it can also produce more false positives. A less sensitive system may reduce unnecessary alerts, but it can increase the chance of missing real attacks.
There is no single configuration that works perfectly for every organization. Security teams need to adjust IDS settings based on network size, business needs, important assets, traffic patterns, and available security resources.
Why Understanding What Security Tradeoffs Occur While Using IDS Matters?
Understanding what security tradeoffs occur while using IDS helps cybersecurity students and professionals make better security decisions.
An IDS is useful because it provides visibility into suspicious network behavior. However, it should not be treated as a perfect security solution. It works best as one layer of a broader security strategy.
Organizations can combine IDS with firewalls, endpoint protection, access controls, vulnerability management, security monitoring, and incident response processes. This layered approach can reduce the weaknesses of relying on one security tool.
Also explore our Course : Ethical Hacking Course
What Security Tradeoff Occurs While Using IDS Due to False Positives?
One important part of what security tradeoffs occur while using IDS is the problem of false positives. A false positive occurs when an IDS identifies normal or harmless activity as a possible threat.
For example, a normal network connection may look unusual because it does not match the expected traffic pattern. The IDS may then create an alert even though no attack has occurred.
Too many false positives can cause:
-
Alert fatigue: Security teams receive too many warnings.
-
Time loss: Analysts spend time investigating harmless events.
-
Delayed investigation: Important alerts may be missed among many low-priority alerts.
-
Higher workload: Teams need more time to review and classify alerts.
Organizations therefore need to tune IDS rules carefully. Reducing unnecessary alerts can make security operations more efficient, but rules that are too relaxed may allow some threats to go unnoticed.
What are the False Negatives and Their Impact on IDS Security
Another major part of what security tradeoffs occur while using IDS involves false negatives. A false negative happens when an IDS fails to detect an actual attack.
This can happen when attackers use new techniques, modify malicious traffic, or take advantage of weaknesses that detection rules do not recognize.
False negatives can result in:
-
Undetected attacks: Malicious activity may pass through monitoring systems.
-
Longer attacker access: Attackers may remain inside a network without being detected.
-
Data loss: Sensitive information may be accessed or stolen.
-
Delayed response: Security teams may not know that an attack is taking place.
This shows why organizations cannot simply reduce alerts by making IDS rules less sensitive. Doing so may reduce false positives but increase the risk of missing real attacks.
What Security Tradeoff Occurs While Using IDS and System Performance?
Another answer to what security tradeoffs occur while using IDS is the balance between monitoring depth and system performance.
An IDS needs resources to inspect network traffic, compare activity with security rules, record events, and generate alerts. Monitoring large amounts of traffic can increase processing and storage requirements.
Organizations may therefore need to balance:
-
How much network traffic is inspected.
-
How many detection rules are active.
-
How much data is stored in security logs.
-
How quickly alerts need to be processed.
-
How much hardware and computing capacity is available.
Deep monitoring can provide more security information, but it may require more resources. A lighter configuration may reduce overhead but provide less visibility.
How to Manage What Security Tradeoff Occurs While Using IDS?
Organizations can manage what security trade-offs occur while using IDS by carefully configuring and maintaining their detection systems.
Some useful practices include:
-
Create a normal traffic baseline: Understand what normal network behavior looks like.
-
Tune detection rules: Remove unnecessary rules and adjust overly sensitive ones.
-
Prioritize important alerts: Focus attention on threats affecting critical systems.
-
Update signatures: Keep detection patterns updated for known threats.
-
Use multiple security layers: Combine IDS monitoring with firewalls, endpoint security, and other controls.
-
Review alerts regularly: Study previous alerts to identify patterns and improve detection accuracy.
These steps can help security teams improve detection without creating an unmanageable number of alerts.

FAQs
What Security Tradeoff Occurs While Using IDS?
How Do False Positives Affect IDS Security?
Why Are False Negatives Dangerous When Using IDS?
How Does an IDS Detect Suspicious Network Activity?
How Can Organizations Reduce the IDS Security Tradeoff?


Get Free Counselling Today
and Clear up all your Doubts
 Live & recorded classes available at easeDashboard for progress trackingLakhs of practice questions