CCNA Security Syllabus in 2026: Topics and Network Security Concepts to Learn
 Hardik Gupta25 Sept, 2026
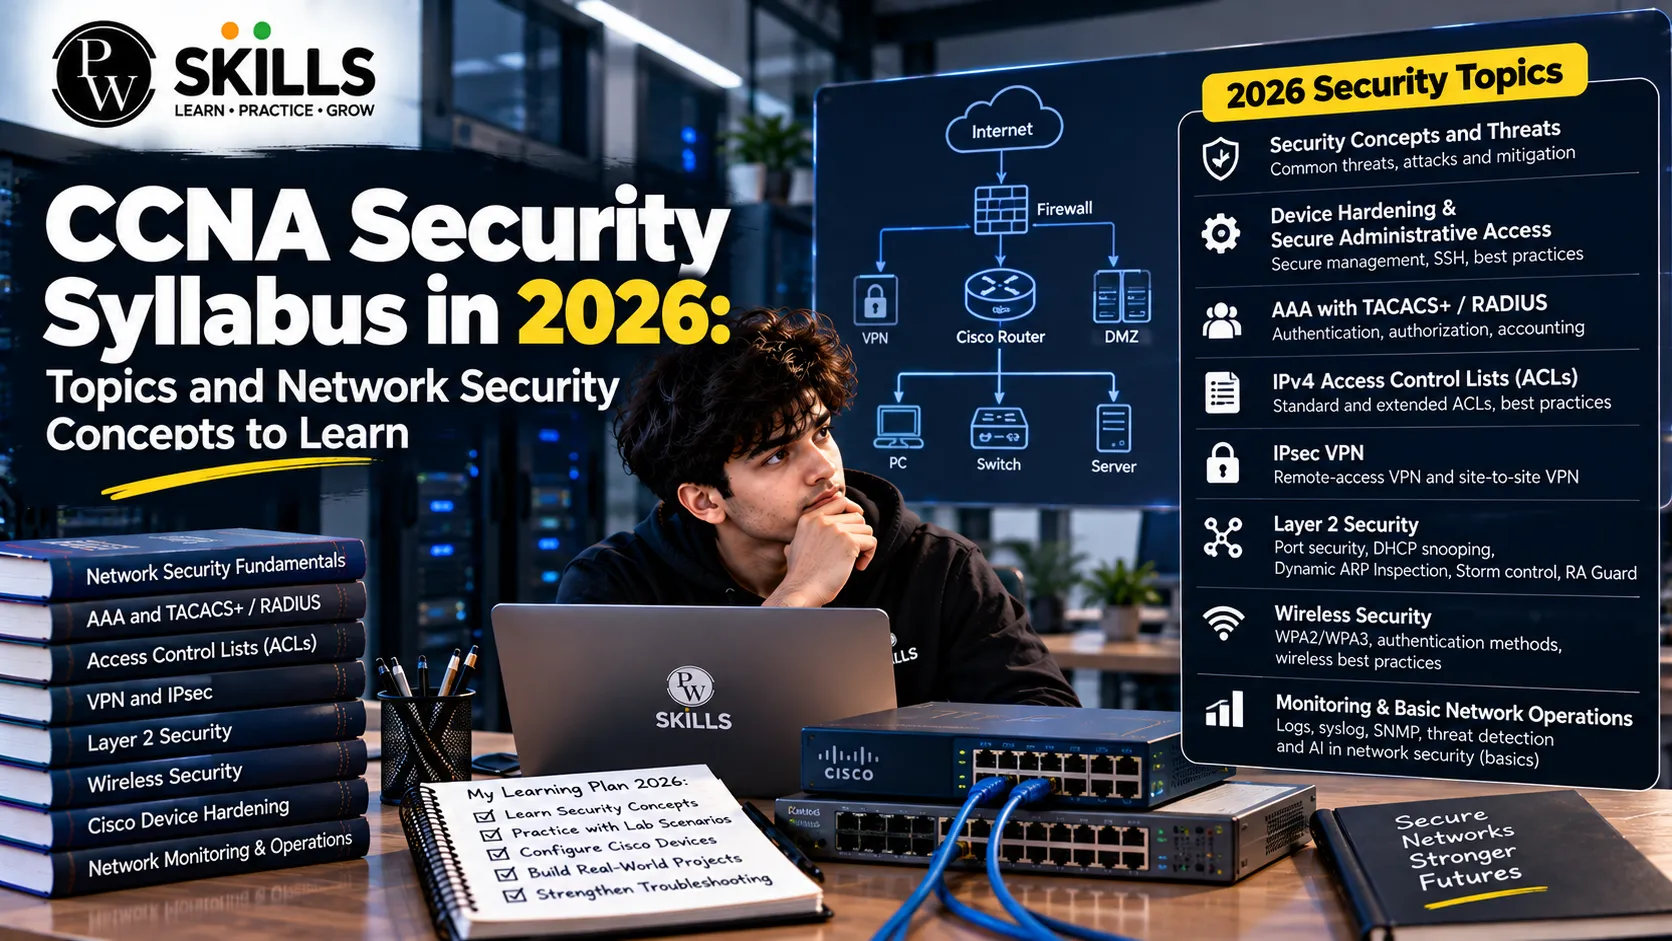
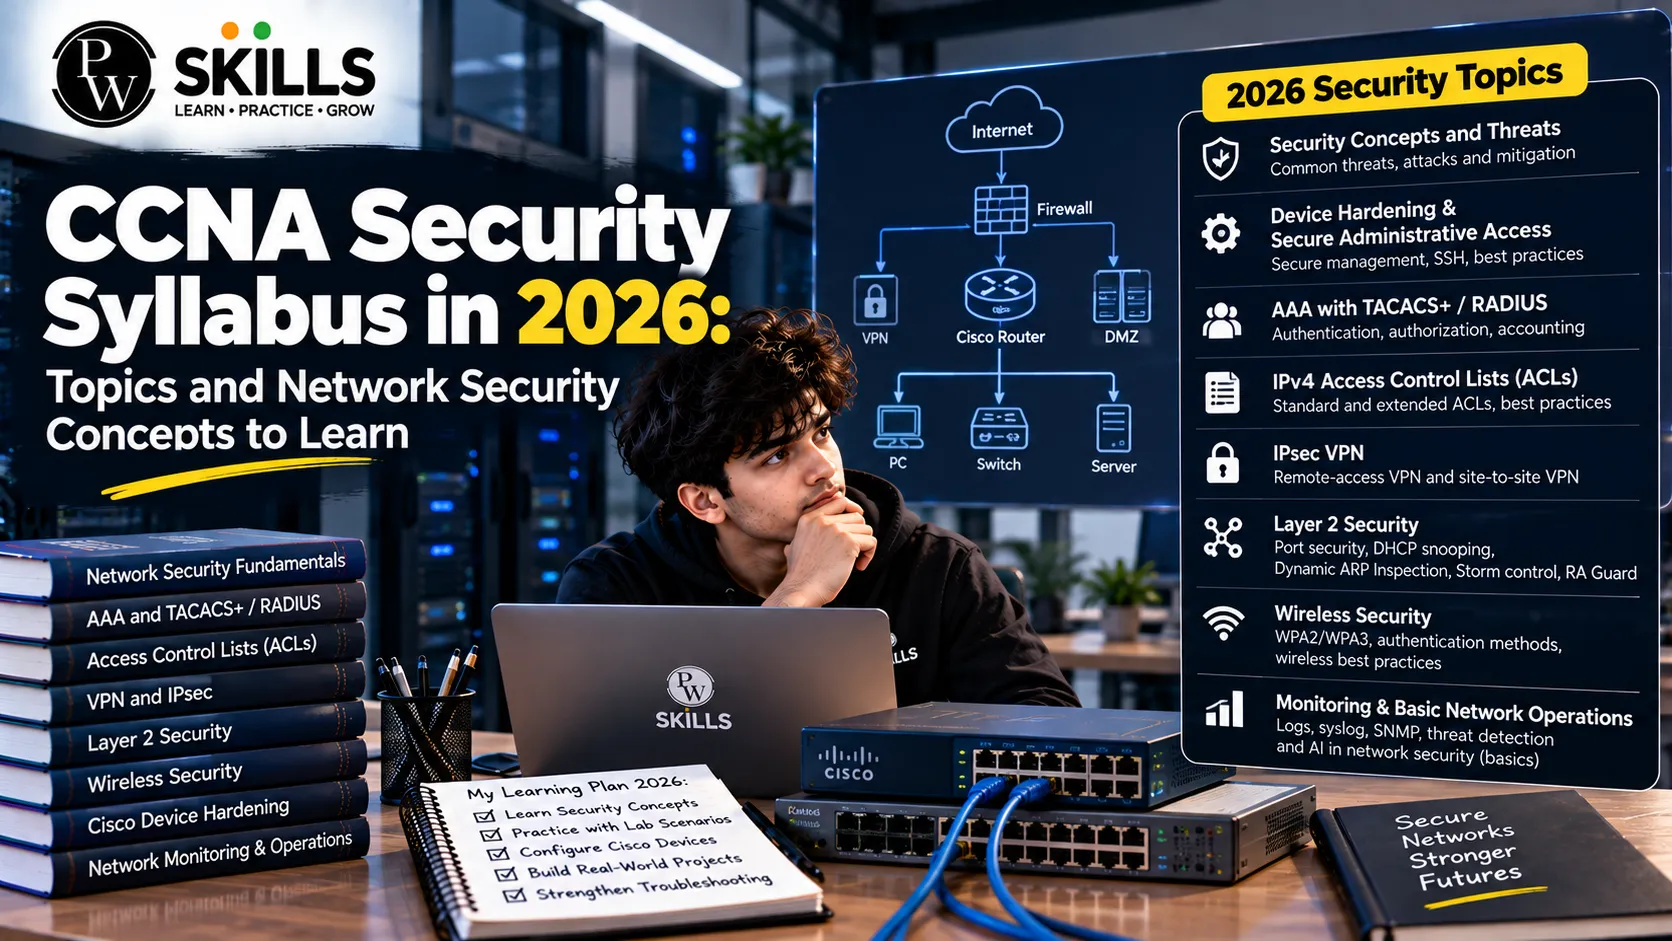
Mastering the CCNA security syllabus requires a solid understanding of modern defense mechanisms and core protocols. Learners often struggle to map out the exact modules needed to pass industry assessments.
Beginners should first build strong networking basics and then practise security concepts through hands-on labs. Combining CCNA security topics, practical skills, and a cybersecurity certification can help learners prepare for network and security roles. This article breaks down the essential study areas for technical aspirants.
Overview of CCNA Security Syllabus
The syllabus of CCNA Security covers important network security concepts needed to protect devices, networks, and data from common cyber threats. It includes topics such as device hardening,
AAA authentication, Layer 2 security, encryption, VPNs, firewalls, and intrusion prevention. Learning these topics helps students build a strong foundation in network defense and prepare for security-focused networking roles.
What Are the Network Basics in the CCNA Security Syllabus?
Before learning advanced security controls, students should understand how networks work. A strong networking foundation makes it much easier to understand why a particular security control is needed.
Start with:
-
IP addressing and subnetting
-
Ethernet and switching basics
-
VLANs
-
Routing fundamentals
-
TCP/IP concepts
-
Common network protocols
-
Network devices and their functions
-
Basic troubleshooting
Once these concepts are clear, learners can understand how attackers may misuse network services and how administrators can protect them.
For example, knowing how DHCP works makes it easier to understand DHCP snooping. Understanding VLANs also makes Layer 2 attacks and VLAN security controls easier to learn.
How Does the CCNA Security Syllabus Cover Device Security?
One of the first security tasks for a network administrator is protecting the devices that control the network. Routers and switches contain important configuration information, so unauthorised access can create serious problems.
Important areas include:
Secure Device Access
Learn how to protect console, VTY, and privileged access. Strong passwords, secure authentication, and appropriate access permissions help reduce unauthorised administrative access.
Device Hardening
Device hardening means reducing unnecessary security risks. This can include disabling unused services, limiting management access, using secure protocols, and keeping device software updated.
AAA
AAA stands for Authentication, Authorization, and Accounting.
-
Authentication: Checks who the user is.
-
Authorization: Determines what the user is allowed to do.
-
Accounting: Records user activity.
Learners should also understand the basic purpose of technologies such as RADIUS and TACACS+ and where centralised authentication can be useful.
What Layer 2 Topics Are in the CCNA Security Syllabus?
Network security is not limited to firewalls. Attackers can also target local switching environments.
Important CCNA security topics at Layer 2 include:
-
Port security
-
DHCP snooping
-
Dynamic ARP Inspection
-
IP Source Guard
-
VLAN security
-
MAC address protection
-
Spanning Tree security concepts
These controls help reduce risks such as unauthorised devices, DHCP attacks, ARP spoofing, and certain types of local network abuse.
Students should not only memorise configuration commands. They should understand the problem each feature is designed to solve.
For example, DHCP snooping builds trust around DHCP traffic, while Dynamic ARP Inspection can use DHCP snooping information to help validate ARP messages.
How Does the CCNA Security Syllabus Cover Encryption and VPNs?
Protecting information while it moves across a network is another important security area.
Students should understand the difference between:
-
Encryption
-
Hashing
-
Authentication
-
Digital signatures
-
Digital certificates
-
Asymmetric encryption
The goal is to understand what each technology does rather than simply memorising technical names.
VPNs are another important area. Learners should understand how a Virtual Private Network creates protected communication over an untrusted network.
Security-focused networking study can include:
-
VPN concepts
-
Site-to-site VPNs
-
Remote-access VPNs
-
IPsec fundamentals
-
Authentication and encryption in secure tunnels
These concepts are useful for understanding how organisations protect communication between offices, users, and network resources.
How Does the CCNA Security Syllabus Cover Firewalls?
Firewalls control network traffic based on defined security rules. Students preparing for a broader network security syllabus should understand how different filtering methods work.
Key areas include:
Access Control Lists
ACLs can be used to permit or deny traffic based on conditions such as source and destination addresses, protocols, and ports.
Stateful Firewalls
A stateful firewall keeps track of active connections. This allows it to make traffic decisions using information about the connection state.
Security Zones
Network segmentation can separate public-facing systems, internal users, servers, and other resources. This can reduce the impact of a security incident.
Firewall Rules
Learners should understand the importance of specific rules, correct rule order, and the principle of allowing only required traffic.
Practical labs are particularly useful here because students can see how changing a rule affects network communication.
How Does the CCNA Security Syllabus Cover Threat Detection?
Prevention is only one part of network security. Organisations also need to monitor systems and identify unusual activity.
Students can learn about:
-
Syslog
-
Network traffic monitoring
-
NetFlow concepts
-
Packet captures
-
Intrusion detection
-
Intrusion prevention
-
Basic security alerts
-
Log analysis
Tools such as Wireshark can help learners inspect network packets and understand what is happening during communication.
The aim is not to become a security operations expert immediately. Instead, students should develop the ability to recognise unusual traffic and understand where further investigation may be required.
Also Check : Ethical Hacking Course
What Modern Security Concepts Are in the CCNA Security Syllabus?
After learning the basic controls, students can explore broader security ideas used in modern organisations.
Zero Trust
Zero Trust follows the idea that access should not automatically be trusted simply because a user or device is inside a network.
Important principles include identity verification, least-privilege access, and continuous evaluation of access requests.
Network Segmentation
Segmentation divides a network into separate areas. This can help limit access between systems and reduce lateral movement if one device is compromised.
Endpoint Security
Network protection also depends on the devices connected to the network. Patch management, secure configurations, endpoint monitoring, and access controls can all contribute to stronger security.
These topics help learners connect traditional network security with current enterprise security practices.
How to Practise the CCNA Security Syllabus With Labs?
Reading about security controls is useful, but networking is a practical field. Students should spend time creating small network labs and testing different configurations.
A useful practice setup can include:
-
Router and switch configurations
-
VLAN creation
-
Secure management access
-
AAA configuration exercises
-
ACL practice
-
Port security
-
DHCP snooping
-
Basic VPN concepts
-
Packet analysis
-
Troubleshooting exercises
Virtual labs and network simulators can make practice easier when physical networking equipment is not available.
After completing each lab, write down what was configured, why it was required, and what happened when the configuration was changed. This develops problem-solving skills instead of command memorisation.
How to Follow a CCNA Security Syllabus Study Plan?
Trying to learn every security concept at once can become confusing. A staged plan makes the process easier.
Stage 1 – Networking Basics:
Learn IP addressing, subnetting, switching, routing, VLANs, and common protocols.
Stage 2 – Device Protection:
Study secure management, device hardening, passwords, and AAA.
Stage 3 – Layer 2 Security:
Practise port security, DHCP snooping, Dynamic ARP Inspection, and related controls.
Stage 4 – Secure Communication:
Learn encryption basics, authentication, certificates, VPNs, and IPsec concepts.
Stage 5 – Traffic Protection:
Study ACLs, firewalls, segmentation, and traffic filtering.
Stage 6 – Monitoring:
Learn logging, packet analysis, traffic monitoring, and basic threat detection.
Stage 7 – Hands-On Practice:
Build labs, troubleshoot problems, and practise security configurations repeatedly.
This order helps learners build each new skill on top of an existing networking foundation.
How Can the CCNA Security Syllabus Support Your Career?
A networking or cybersecurity certification can help demonstrate that you have studied important technical concepts. However, certification alone does not replace practical skills.
Employers may also look for experience with networking, troubleshooting, security tools, and hands-on labs.
Depending on experience and additional skills, learners can work toward roles such as:
-
Network Support Engineer
-
Network Administrator
-
Junior Network Security Engineer
-
Security Operations Analyst
-
IT Security Associate
-
Network Security Analyst
A good career plan combines certification preparation with practical projects, troubleshooting practice, and continued learning.

FAQs
What subjects are covered in the CCNA security syllabus?
Why are CCNA security topics important for network engineers?
What should I learn before starting a network security syllabus?
How does networking security protect an enterprise network?
How does a cybersecurity certification help with a networking career?


Get Free Counselling Today
and Clear up all your Doubts
 Live & recorded classes available at easeDashboard for progress trackingLakhs of practice questions